An auditor asks for evidence that every terminated employee lost access within a defined window. The answer lives in a spreadsheet, three ticketing queues, and the memory of one overworked IT administrator. If that sounds familiar, the problem isn't your team. Manual processes can't keep pace with the number of identities, applications, and cloud services most enterprises now run.
This article explains what identity governance is, where automation helps, where it doesn't, and how executives can evaluate it without buying into hype.
What Is Identity Governance, and Why Does Automation Matter?
Identity governance (often called IGA, or Identity Governance and Administration) is the discipline of deciding who should have access to which systems and data, proving that those decisions are correct, and correcting them when they aren't. It sits within the broader field of identity and access management (IAM). IAM handles authentication and access mechanics. Governance handles the question, "Should this person still have this access?"
Automation matters because governance fails mostly through volume and delay, not bad intent. People change roles, contractors come and go, and applications multiply. Each change creates a decision someone must make, and when those decisions queue up, access drifts away from what the business intended.
The Core Identity Governance Challenges
Most organizations struggle with the same few problems:
Where Intelligent Automation Delivers the Most Value
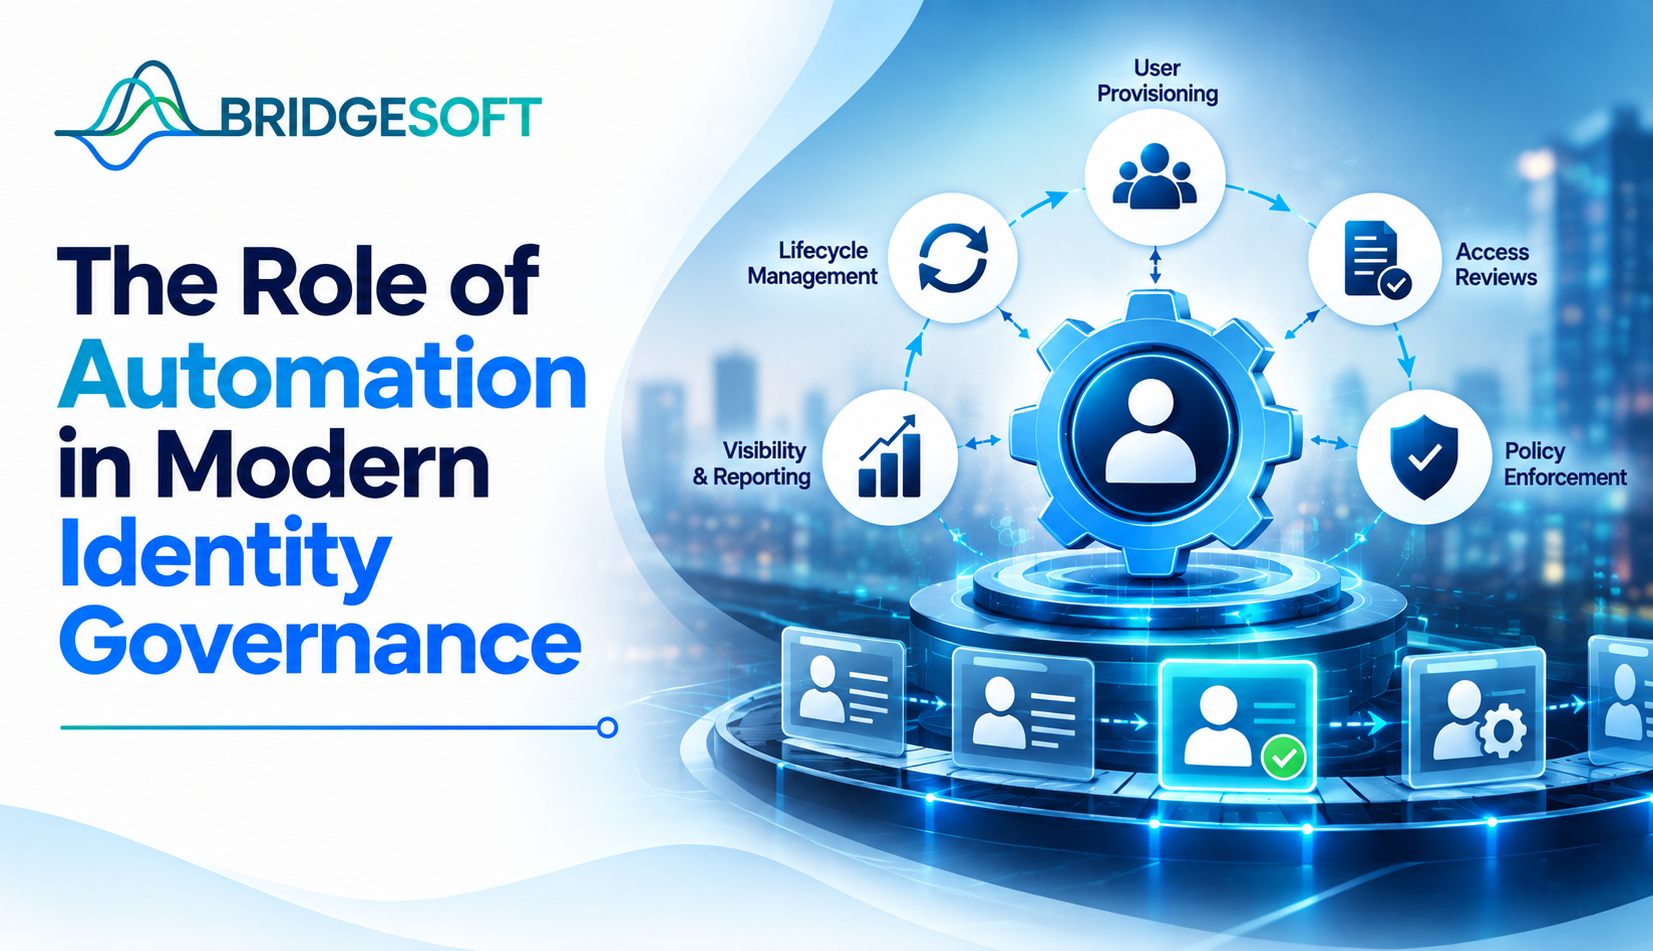
Lifecycle provisioning. When your HR system records a hire, transfer, or termination, automation can grant or revoke baseline access immediately, based on role and department. This is usually the best starting point because the rules are clear and the payoff is visible.
Smarter access reviews. Intelligent automation can analyze historical access patterns, peer-group behavior, and usage data to flag unusual access—such as permissions that peers in the same role don't hold or access that has gone unused for months. Reviewers can then focus their attention where risk is highest.
Policy enforcement and separation of duties. Rules like "the person who creates a vendor can't also approve payment" can be checked automatically at request time, not discovered during an audit.
Continuous evidence. When approvals, changes, and revocations are logged as they happen, audit preparation shifts from a project to a report.
What Does AI for Identity Add?
Rules-based automation handles what you can define in advance. AI for identity helps with what you can't easily write rules for: spotting outlier access, suggesting role structures from existing permission patterns, and ranking which access requests deserve human scrutiny.
The limits matter, though. AI recommendations are only as good as the underlying data, and messy entitlement data produces confident-looking but wrong suggestions. For high-impact decisions, such as privileged or financial-system access, a human should still approve. Use AI to prioritize reviewer attention, not replace accountability. This is where the next frontier in identity governance is heading: more continuous, risk-aware governance, with people reserved for judgment calls.
When Automation Works, and When It Doesn't
| Situation | Automation fit |
| Clear roles, authoritative HR data | Strong |
| High-volume, low-risk access (email, collaboration tools) | Strong |
| Poorly documented applications with no connector or API | Weak until onboarded |
| Role definitions disputed across departments | Fix the policy first |
| Privileged or highly sensitive access | Automate evidence, keep human approval |
The most common mistake is automating a broken process. If nobody agrees on what a "sales manager" should access, automation will enforce the disagreement faster.
A Practical Starting Path
For CFOs and COOs, the ROI case usually rests on reduced manual effort, faster onboarding productivity, and lower audit cost. Model these against your own numbers, not industry averages.
Common Mistakes to Avoid

Bridgesoft helps organizations improve identity visibility, strengthen Identity Governance, streamline Identity Access Management, and modernize identity processes across complex enterprise environments.
Book a Free DemoConclusion
Automation doesn't replace identity governance. It makes governance sustainable. Start with clean data and clear roles, automate the predictable processes first, then layer in analytics where they sharpen human decisions. If you're evaluating where your program stands, assessing your current access lifecycle is a practical first step.
IAM manages authentication and access mechanics, such as logins and single sign-on. Identity governance oversees whether access is appropriate, reviewed, and compliant. Governance is a layer within a mature IAM program.
No. Routine provisioning and evidence collection can be, but policy decisions and high-risk approvals need human accountability.
It depends on application count, data quality, and organizational readiness. A phased rollout, beginning with lifecycle automation, typically shows results sooner than a single large deployment.
Yes. Consistent enforcement and automatic logging make it easier to demonstrate controls required by frameworks such as SOX, HIPAA, and SOC 2. Compliance still depends on well-defined policies.
It helps with prioritization and anomaly detection, but its output depends on data quality and should be validated by people.