In today’s rapidly evolving digital ecosystem, organizations are under constant pressure to modernize their IT infrastructure while maintaining business continuity. Many enterprises rely on legacy systems that power essential operations developed years ago. While these systems provide significant operational value, they often struggle to meet current security expectations, cloud strategies, and compliance requirements. Modern Identity Access Management solutions help organizations overcome these challenges by modernizing security, improving compliance, and supporting continuous operations.
As organizations accelerate digital transformation initiatives, the challenge is no longer just about adopting new technologies. Instead, it is about ensuring seamless integration between existing legacy applications and modern identity platforms. To accomplish this, businesses require secure, scalable, and intelligent identity frameworks that can bridge the gap between traditional infrastructure and modern cloud ecosystems without disrupting ongoing operations.
To address these evolving needs, modern Identity Access Management platforms are designed to provide centralized control, enhanced visibility, and stronger security across hybrid environments. By integrating legacy systems with advanced identity solutions, organizations can create a unified access ecosystem that improves user experience, strengthens compliance, and reduces operational complexity.
Legacy systems often operate in isolated environments with outdated authentication methods, fragmented user directories, and limited support for modern security protocols. While these systems remain essential for many business processes, they can become major obstacles when organizations attempt to implement enterprise-wide digital security strategies.
Traditional systems typically lack advanced Identity Governance capabilities, making it difficult for organizations to monitor who has access to what resources, why that access exists, and whether it still aligns with current business requirements. Over time, unmanaged permissions and excessive access privileges increase security risks and create compliance challenges.
Additionally, legacy applications may not support cloud-native authentication mechanisms such as Single Sign-On (SSO), Multi-Factor Authentication (MFA), or federation standards. This creates fragmented user experiences in which employees manage multiple credentials across disconnected systems, ultimately reducing productivity and increasing the risk of credential misuse.
Modern identity platforms address these challenges by securely connecting old and new technologies. This enables businesses to enhance security, update access management procedures, and comply with new rules without completely redesigning their existing infrastructure.
Organizations today require more than just authentication systems. They need intelligent, policy-driven identity ecosystems that can manage users, applications, devices, and data access in real time. Modern Identity Access Management solutions deliver this flexibility by providing centralized identity controls across on-premises, cloud, and hybrid environments.
By integrating IAM solutions with legacy systems, organizations establish unified access policies, improved governance, and automated provisioning. This approach helps maintain ongoing operations while strengthening security, reducing manual processes, and meeting regulatory requirements.
One of the most critical benefits is the implementation of Role-based access control (RBAC). RBAC allows organizations to assign permissions based on user roles rather than managing access for each employee individually. This not only simplifies administration but also reduces the risk of unauthorized access by ensuring users receive only the permissions necessary for their responsibilities.
For example, employees in finance departments can automatically gain access to financial systems, while HR teams receive permissions aligned with employee management applications. When integrated with legacy systems, RBAC creates a structured and scalable security framework that minimizes manual intervention and reduces administrative overhead.
[What is Intelligent Identity Governance?]
As cyber threats continue to evolve, organizations must move beyond traditional perimeter-based security models. Identity has become the new security perimeter, making Identity Governance a critical component of enterprise cybersecurity strategies.
Modern identity platforms enable organizations to establish governance frameworks that continuously monitor user access, detect anomalies, and enforce compliance policies. Businesses obtain full visibility into their identity ecosystem through automated access assessments, approval workflows, and audit reporting.
When legacy systems are integrated into a centralized Identity Governance framework, organizations can eliminate access silos and create consistent security controls across all applications. This unified visibility helps security teams quickly identify orphaned accounts, excessive permissions, and outdated access rights that could otherwise become potential attack vectors.
Digital transformation is accelerating across industries, but organizations still rely on legacy applications for key business operations. These systems often lack the security features needed for modern cybersecurity and compliance. With cloud adoption, hybrid environments, and remote work, securing legacy applications is now a top IT and security priority.
Modern Identity Access Management (IAM) transforms legacy systems by integrating them into a centralized identity framework. This strengthens security, enhances governance, simplifies access, and supports scalability, bridging traditional infrastructure with future-ready environments without disrupting business operations.
Legacy applications were designed in a different era, before today’s standard cloud computing, security threats, and regulations. Many use outdated authentication, local credential storage, shared admin accounts, and manual processes—creating serious security gaps for modern enterprises.
One of the biggest challenges organizations face with legacy systems is the lack of centralized visibility into identities (knowing who has access to what). Employees often manage multiple usernames and passwords across applications, which increases password fatigue and the risk of credential compromise. In many cases, IT teams struggle to track who has access to specific systems, whether that access is still required, and whether excessive permissions exist within critical applications. Without proper Identity Governance (policies and tools to control user access), organizations lose the ability to effectively control and monitor user access across the enterprise.
Compliance requirements add another layer of complexity. Regulations such as GDPR (General Data Protection Regulation), HIPAA (Health Insurance Portability and Accountability Act), SOX (Sarbanes-Oxley Act), and ISO standards (international security and quality benchmarks) require organizations to implement strict access controls, maintain audit trails, and demonstrate accountability for user permissions. Legacy applications rarely provide these capabilities natively, making IAM implementation essential for organizations that need to meet modern compliance expectations while reducing operational risks.
Modern IAM integrates legacy systems into a unified security framework. Older applications can join a centralized identity environment that supports secure authentication, access control, and automated management—improving security without disrupting operations.
A modern IAM solution centralizes authentication policies, enabling users to securely access multiple systems through Single Sign-On (SSO) and Multi-Factor Authentication (MFA), improving the user experience, security, and operational efficiency.
Identity Governance is increasingly important as organizations grow employees, contractors, vendors, machines, bots, APIs, and AI agents all need secure, controlled access. Without governance, risks like excessive privileges, orphaned accounts, and threats increase.
Integrating Identity Governance into legacy environments improves access visibility, automates reviews, and enforces policy-driven controls. This visibility is vital for compliance and risk management in regulated industries.
Identity Federation
Modern IAM uses multiple methods for integrating legacy applications. Identity federation allows users to authenticate with a centralized provider while accessing older systems, creating a seamless experience while enabling consistent security policies.
Directory Synchronization
Directory synchronization is key for legacy integration. Older systems often rely on on-premises directories like Active Directory or LDAP. Modern IAM can synchronize identities across all environments, improving consistency and reducing administrative effort.
Access Gateway Solutions
IAM access gateways add a security layer in front of legacy applications, allowing modern authentication methods without modifying the applications. Gateways introduce MFA, adaptive authentication, and session policies, even for systems that originally lacked these features.
API-Based Integration
API-based integration lets legacy applications join centralized provisioning, role management, and audit workflows. Automated identity management reduces manual work while improving consistency and security.
Privileged Access Management (PAM)
Privileged Access Management is vital for legacy environments. Many older systems use poorly secured privileged accounts. Integrating PAM secures credentials, automates password rotation, monitors sessions, and enforces least-privilege policies—cutting insider threat risk.
Modern IAM for legacy systems brings more than just security. Automated onboarding and offboarding improve efficiency, unified authentication simplifies user experience, and centralized governance streamlines audits and compliance. A scalable identity foundation supports digital transformation.
Effective IAM implementation needs planning. Legacy setups are complex, with undocumented dependencies and inconsistent models. Organizations must first assess identity structures, application dependencies, privileged accounts, and governance gaps before modernizing.
For years, IAM served as the backbone of enterprise security, ensuring appropriate access for the right people in a world where identities were static and human.
Today, enterprises operate in an ecosystem where AI agents—such as virtual assistants handling HR tasks, autonomous cybersecurity bots, and automated customer support chatbots—act autonomously, APIs communicate continuously, and machines outnumber humans. Identity is no longer a static attribute—it’s dynamic, distributed, and increasingly intelligent.
And in this new reality, traditional IAM isn’t just struggling—it’s fundamentally breaking.
Many organizations believe identity is controlled because users can log in, and audits occur. But the reality is more complex.
Modern environments teem with non-human identities—service accounts, bots, APIs, and AI agents. These entities work at machine speed, interact across systems, and often evolve autonomously.
Traditional IAM, designed around human workflows, simply cannot keep pace.
This creates an illusion of security: systems appear protected, but critical access remains unmonitored and vulnerable.
AI agents represent a profound shift in how work gets done.
They are not just executing instructions—they are:
They behave like users but without human oversight.
Yet, most legacy IAM systems fail to:
This gap introduces a new category of risk—one that is invisible to traditional security models.
[Discover why most implementations fall apart → Why Most IAM Projects Fail]
Without this clarity, governance becomes reactive rather than proactive.
Tech adoption multiplies identities swiftly; each application or AI model adds new access points.
This leads to identity sprawl—a state where identities are:
Industry insights note 85% of organizations face identity sprawl risks; machine identities often outnumber human ones 10:1.
In such an environment, even a single unmanaged identity can become a gateway for security breaches.
Regulatory expectations now demand continuous, real-time assurance—not just periodic audits.
However, traditional IAM systems were built for:
This gap leaves organizations unable to meet regulatory demands.
The result? Increased audit pressure, higher compliance costs, and greater exposure to risk.
Organizations must rethink identity as an intelligent, living ecosystem—not just a system.
Modern identity governance requires a shift toward:
The future of identity lies in orchestration—a centralized approach that connects systems, enforces policies, and automates workflows across the enterprise.
Instead of managing identities in isolation, organizations need a platform that:
This orchestration layer becomes the foundation for:
AI is advancing faster than most companies can keep up with. Every new AI deployment introduces:
Without modern identity governance, these risks accumulate silently—until they surface as security incidents, compliance failures, or operational disruptions.
Acting now reduces risk and builds strategic advantage for secure innovation.
Traditional IAM's failures are a signal of necessary change.
A signal that identity must evolve alongside technology.
A signal that governance must become intelligent, automated, and unified.
A sign that organizations capable of observing, recognizing, and controlling all identities—human or non-human will own the future.
Platforms like Bridgesoft Identity Gateway are built for this new era—where identity extends beyond users to include machines and AI.
By combining:
They enable organizations to move from fragmented IAM to holistic identity orchestration.
Transform your approach today and secure your organization's future.
Book a Demo
#IdentityGovernance #IAM #CyberSecurity #AI #AIAgents #ZeroTrust #IdentityManagement #MachineIdentity #DigitalTransformation #AccessControl #FutureOfSecurity #Bridgesoft
Identity and Access Management (IAM) is no longer just a layer of security—it has evolved into a critical business enabler. From onboarding employees efficiently to ensuring regulatory compliance and enabling secure digital transformation, IAM sits at the heart of modern enterprise operations.
Despite its importance, many organizations struggle with a persistent, often underestimated challenge: slow IAM deployment.
At first glance, implementation delays may appear manageable—just a few weeks added to timelines or minor integration setbacks. However, as these delays accumulate, they begin to create ripple effects across the organization. What starts as a technical delay gradually becomes a business problem, affecting security, productivity, compliance, and overall performance.
To truly understand how to avoid these outcomes, it’s important to first recognize the root causes behind why IAM Projects fail and how organizations can implement IAM successfully with the right strategy.
Slow IAM deployment is not just about missed deadlines—it often reflects deeper inefficiencies in an organization’s technology and processes.
It can manifest in several ways: delayed employee onboarding, prolonged application integrations, heavy reliance on manual provisioning, and extended implementation cycles that far exceed initial expectations. These inefficiencies are typically rooted in legacy systems, a lack of integration planning, and the absence of a structured implementation roadmap.
Organizations that take the time to build a clear IAM roadmap and prioritize early integration are better positioned to avoid these delays and achieve a more streamlined implementation journey.
One of the most immediate and critical consequences of slow IAM deployment is the increased exposure to security risks. When IAM systems are only partially implemented, users often retain access privileges longer than necessary, and manual errors become more frequent.
Delayed deprovisioning and lack of centralized control create gaps that can be exploited, increasing the likelihood of unauthorized access or data breaches. Over time, these vulnerabilities can have serious financial and reputational consequences for the organization.
Beyond security, slow IAM directly impacts the day-to-day productivity of employees and teams. When access to applications and systems is delayed, employees are unable to perform their roles efficiently.
IT teams, on the other hand, are often burdened with repetitive manual tasks such as provisioning and access approvals. This not only slows down business workflows but also diverts valuable resources away from more strategic initiatives.
The result is a workplace environment where inefficiencies become normalized, and both employees and IT teams experience growing frustration.
IAM is often viewed as a long-term investment in security and efficiency. However, when deployment is slow, it begins to behave more like an ongoing operational expense.
Delays lead to extended development efforts, continuous rework, and increased reliance on manual processes. Organizations may find themselves allocating additional resources to maintain incomplete systems, driving up costs without delivering proportional value.
In such scenarios, the true cost of IAM is not in its implementation—but in its delay.
IAM plays a central role in maintaining regulatory compliance and ensuring audit readiness. When implementation is delayed, organizations struggle to establish complete audit trails, enforce access governance policies, and generate consistent reports.
These gaps can lead to compliance failures, especially in highly regulated industries where visibility and accountability are critical. The longer the IAM deployment is delayed, the more difficult it becomes to meet regulatory requirements and avoid potential penalties.
IAM is a foundational component for broader digital transformation efforts, including cloud adoption, automation, and Zero Trust security models.
When IAM deployment is slow, it creates a bottleneck that impacts these initiatives. Organizations may find themselves unable to move forward with modernization efforts because the underlying identity infrastructure is not yet mature.
In this way, IAM delays do not just affect security—they slow down the organization’s ability to innovate and compete in a digital-first world.
In today’s fast-paced work environment, users expect seamless and immediate access to the tools they need. Slow IAM processes, however, often lead to login issues, access delays, and inconsistent user experiences.
When employees are unable to access systems efficiently, they may turn to unauthorized tools or workarounds—leading to the rise of shadow IT. This not only undermines security but also creates additional governance challenges for the organization.
A major contributor to slow IAM deployment is the difficulty of integrating with legacy systems. Many enterprises operate with outdated platforms that lack modern APIs or standardized integration capabilities.
IAM projects rarely fail because organizations lack intent or investment. In fact, most enterprises begin their IAM journey with clear objectives—improving security, ensuring compliance, and enabling seamless access across systems. However, the real challenge lies in execution.
From integration complexities to data inconsistencies and organizational misalignment, IAM implementation often becomes more complicated than expected. The good news is that these challenges are not unavoidable. With the right strategy, planning, and governance model, organizations can significantly accelerate IAM deployment while reducing risk.
If you haven’t yet explored the root causes, start here: Why IAM Projects Fail (Real Reasons Enterprises Struggle)
Every successful IAM implementation begins with a well-defined roadmap. Without a clear direction, even the most advanced tools and technologies can lead to fragmented outcomes.
An effective IAM roadmap provides structure by defining the scope of implementation, breaking the journey into manageable phases, and establishing measurable success criteria. Rather than attempting a large-scale rollout from the start, organizations benefit from taking a phased approach—beginning with pilot deployments, learning from early outcomes, and scaling gradually.
This structured progression not only reduces implementation risk but also builds confidence across stakeholders as tangible results begin to emerge.
Integration is often where IAM projects face the greatest friction. Enterprises operate in complex environments that include a mix of legacy systems, modern applications, and cloud platforms—each with different levels of integration readiness.
Treating integration as a secondary consideration can lead to delays and costly rework. Instead, organizations should evaluate their application landscape early, identify integration challenges, and define a clear strategy for connecting systems.
Modern approaches, including low-code integration platforms and pre-built connectors, are helping organizations simplify this process. By prioritizing integration from the beginning, enterprises can significantly accelerate IAM deployment timelines while reducing technical complexity.
While custom development may seem like a practical solution to address integration gaps, it often creates long-term challenges that outweigh its short-term benefits.
Over time, custom code introduces dependencies that make upgrades more difficult, increase maintenance effort, and reduce overall agility. What begins as a workaround can quickly become a constraint that slows down innovation.
A more sustainable approach is to leverage standardized frameworks, reusable components, and pre-built integrations wherever possible. This not only improves scalability but also ensures that the IAM architecture remains adaptable as business needs evolve.
One of the most overlooked aspects of IAM implementation is the quality of identity data. IAM systems rely on accurate and consistent data to function effectively, however many organizations struggle with duplicate records, outdated access information, and inconsistent role definitions.
Deploying IAM on top of poor-quality data can amplify existing issues, leading to incorrect access provisioning and increased security risks. Instead, organizations should invest time in cleaning and standardizing identity data before scaling their IAM initiatives.
Establishing strong identity governance early creates a solid foundation for automation, compliance, and long-term success.
IAM is not just an IT initiative—it is a business enabler that requires collaboration across multiple functions. Successful implementations depend on alignment between IT, HR, compliance teams, and business stakeholders.
When these groups work in silos, access policies often fail to reflect real business needs, resulting in inefficiencies and user frustration. On the other hand, when organizations foster cross-functional collaboration, IAM becomes more intuitive, effective, and aligned with operational goals.
This alignment ensures that IAM is not only technically sound but also practically relevant to the organization’s day-to-day operations.
Attempting a full-scale IAM rollout in a single phase can introduce unnecessary risk. Complex implementations are more likely to encounter delays, resistance, and unforeseen challenges when approached all at once.
A phased deployment strategy allows organizations to focus on critical applications and key user groups first, delivering immediate value while minimizing disruption. As confidence and maturity increase, the implementation can be expanded to cover additional systems and users.
This incremental approach not only reduces risk but also improves adoption and overall project success.
Compliance should not be treated as a final checkpoint in IAM implementation—it should be embedded into the system from the very beginning.
Organizations must design IAM solutions with built-in audit trails, access governance policies, and reporting capabilities that support regulatory requirements. By taking a proactive approach, enterprises can ensure continuous compliance rather than scrambling to meet audit demands later.
In today’s hyper-connected enterprise ecosystem, identity has quietly become the new control plane for security.
Organizations no longer operate within a single application environment. Instead, they rely on a constantly expanding mix of cloud platforms, SaaS tools, legacy systems, APIs, partner portals, and hybrid infrastructures. While this digital expansion has accelerated innovation, it has also introduced a growing identity challenge — one that traditional Identity and Access Management (IAM) systems were never designed to handle.
According to recent Gartner IAM roadmap insights, the future of enterprise security lies not in deploying more IAM tools, but in integrating identity across the entire digital landscape. This is where the concept of Identity Integration Platforms begins to reshape how modern organizations approach IAM.
Over the past decade, enterprises have adopted multiple identity solutions to address different needs:
While each of these tools solves a specific problem, they often operate in silos — resulting in fragmented identity governance across the enterprise.
This leads to:
In industries like aviation and gaming — where Bridgesoft IAM solutions are increasingly being deployed — managing identity across legacy reservation systems, operational platforms, third-party APIs, and cloud-native applications has become particularly complex.
The traditional IAM approach simply doesn’t scale in these environments.
Gartner IAM roadmap now emphasizes a shift from standalone identity management tools toward integrated identity ecosystems that can unify authentication, authorization, and governance across diverse technology stacks.
Rather than managing identity at the application level, organizations are being encouraged to treat identity as an integration layer — connecting:
This shift reflects a broader move toward identity-first security models, where access decisions are made dynamically based on context, risk signals, and policy orchestration across platforms.
Identity Integration Platforms are designed to bridge the gap between fragmented IAM deployments and modern enterprise infrastructure.
Instead of replacing existing IAM investments, these platforms enable organizations to:
This approach allows enterprises to unify identity operations without disrupting mission- critical systems, which are a crucial requirement for sectors that depend on continuous availability and compliance.
As enterprises continue their digital transformation journeys, identity is becoming deeply embedded in every business transaction — from employee onboarding and customer logins to partner integrations and machine-to-machine communications.
Managing these identities in isolation is no longer sustainable.
By aligning with Gartner IAM trends and adopting Identity Integration Platforms, organizations can:
The future of IAM is no longer about managing identities within applications — it's about integrating identity across ecosystems.
Identity Integration Platforms represent the next phase of the IAM evolution, enabling enterprises to move from fragmented identity management toward a unified, policy-driven identity fabric.
As organizations revisit their IAM roadmap considering Gartner’s strategic direction, investing in identity integration may well become the foundation for scalable, secure digital growth.
Gartner, Develop an IAM Program Roadmap to Deliver Business Value, Steve Wessels, Rebecca Archambault, Brian Guthrie, 2 September 2025.
GARTNER is a registered trademark and service mark of Gartner, Inc. and/or its affiliates in the U.S. and internationally and is used herein with permission. All rights reserved.
In today’s digital enterprise, managing who has access to what is no longer just an IT task—it’s a critical business priority. With organizations operating across cloud platforms, legacy systems, SaaS applications, and remote work environments, Identity and Access Management (IAM) has become the backbone of enterprise security.
However, many organizations struggle with fragmented identity systems, manual provisioning, compliance risks, and delayed application onboarding. This is where a well-structured IAM roadmap becomes essential.
An effective IAM implementation of roadmap helps enterprises transition from reactive access management to a strategic identity-centric security framework. In this guide, we’ll walk through a step-by-step IAM strategy that enterprises can follow to successfully implement and scale IAM across their organization.
Many organizations jump into IAM projects by selecting tools before defining their strategy. This often leads to delays, integration issues, and poor user adoption.
A well-defined IAM roadmap helps enterprises:
Most importantly, it provides a structured IAM implementation roadmap that reduces complexity and ensures long-term scalability.
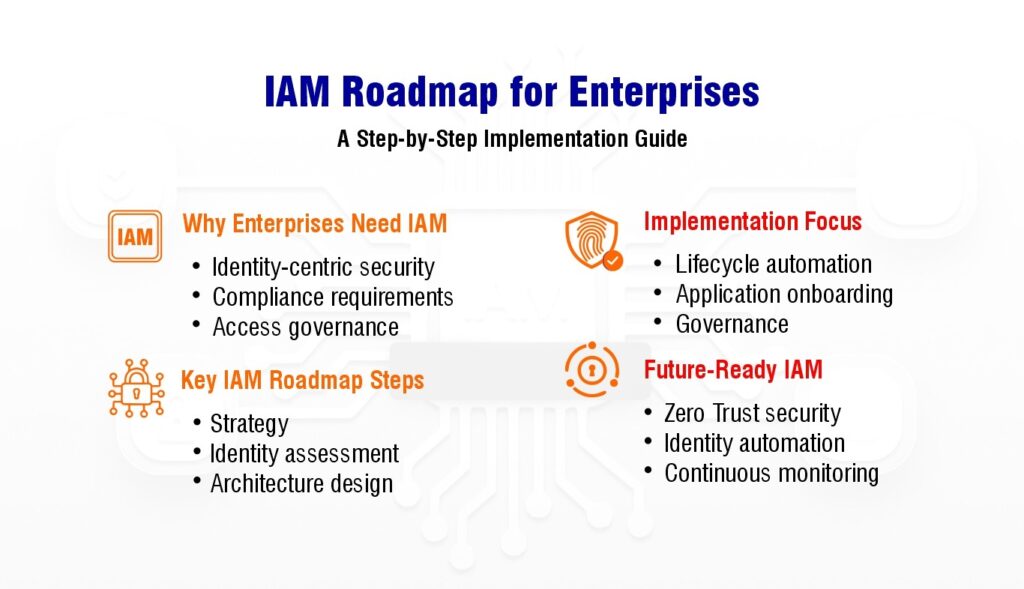
The first step in building an effective IAM strategy is to understand the organization’s security goals and operational needs.
Important factors to consider:
During this stage, enterprises should involve stakeholders from IT, security, compliance, HR, and business units to ensure the IAM roadmap aligns with broader organizational priorities.
A well-defined IAM strategy forms the foundation of a successful IAM implementation roadmap.
Before implementing IAM, organizations must evaluate their existing identity infrastructure.
This assessment typically includes:
Enterprises often discover fragmented identity systems and inconsistent access policies during this phase.
Understanding these gaps helps define the scope of the IAM roadmap and highlights integration challenges early in the implementation process.
Not every application needs to be onboarded into IAM at once. A phased approach ensures smoother implementation and reduces operational risks.
Priorities for organizations should be:
This prioritization becomes a key component of the IAM implementation roadmap, allowing enterprises to achieve quick wins while gradually expanding identity governance coverage.
Once priorities are established, the next step is designing a scalable IAM architecture.
A typical enterprise IAM architecture includes:
Organizations must also plan how to integrate legacy systems, SaaS platforms, and custom applications into the IAM framework.
This is where modern integration solutions—such as identity gateways or automation layers—can significantly simplify application onboarding and reduce integration complexity.
One of the biggest benefits of IAM is automated identity lifecycle management.
This includes managing the entire user journey:
Automating these processes ensures that users receive the right access at the right time while preventing unauthorized access after role changes or employee departures.
A strong lifecycle management strategy is a cornerstone of an effective IAM roadmap.
Regulatory frameworks and internal security policies require organizations to maintain strict access controls.
IAM enables enterprises to enforce:
These capabilities help organizations strengthen governance while simplifying compliance with industry standards.
By integrating governance into the IAM implementation roadmap, enterprises can ensure that identity security aligns with regulatory requirements.
One of the biggest challenges in enterprise IAM projects is integrating diverse applications.
Many legacy systems lack modern APIs or identity connectors, making integration complex and time-consuming.
To address this challenge, organizations can leverage integration platforms that support:
These technologies accelerate application integration and reduce the operational overhead of IAM deployments.
IAM is not a one-time implementation—it’s an ongoing process.
Once the IAM system is deployed, organizations should continuously monitor:
Regular reviews help refine the IAM strategy and ensure the IAM roadmap evolves with business needs, new technologies, and emerging security threats.
Even with a well-planned IAM implementation roadmap, enterprises often face challenges such as:
Addressing these challenges requires both strong IAM governance and flexible integration capabilities that simplify identity automation across enterprise systems.
Tired of IAM Delays Slowing You Down?
Accelerate deployment with a smarter integration strategy.
👉 Schedule a Demo
As organizations adopt cloud platforms, remote work models, and digital ecosystems, identity becomes the new security perimeter.
A future-ready IAM strategy should focus on:
By following a structured IAM roadmap, enterprises can build a secure, scalable identity framework that supports digital transformation while protecting critical business assets.
Implementing IAM is not just about deploying technology—it’s about creating a strategic identity framework that aligns security, compliance, and business operations.
Digital transformation has reshaped how businesses operate, and with it, the concept of identity has evolved. No longer limited to human users, today’s enterprises rely on machine identities non-human entities that authenticate, communicate, and execute critical workflows. From cloud workloads and DevOps pipelines to IoT devices and AI driven automation, machine identities now outnumber human users in many organizations.
Yet, despite their growing importance, these identities often remain unmanaged, overprivileged, and vulnerable making them prime targets for cyberattacks.
What Are Machine Identities?
Machine identities are digital credentials that enable secure authentication and communication for non-human entities. These include:
Unlike human users, machine identities operate silently in the background often with persistent access, excessive privileges, and weak rotation policies. This makes them a goldmine for attackers looking to escalate privileges or move laterally across networks.
Why Machine Identity Governance is Critical Neglecting machine identities leads to security blind spots and compliance risks. High profile breaches often stem from exposed API keys, misconfigured service accounts, or hardcoded credentials. In cloud native environments, where workloads scale dynamically, the risks multiply.
Key challenges include:
Credential sprawl – Uncontrolled accumulation of machine identities with no clear ownership
Privilege creep – Over permissioned service accounts increasing attack surfaces
Manual mismanagement – Secrets stored in plaintext, hardcoded scripts, or shared carelessly
Audit gaps – No visibility into who created an identity, what it accesses, or if it’s still needed
Security teams can’t protect what they can’t see. Without governance, machine identities become invisible and exploitable.
The Expanding Attack Surface
Machine identities now permeate every layer of IT:
Attackers exploit these weak points through credential harvesting, token theft, and privilege escalation. Worse, breaches often go undetected for months because machine activity isn’t logged or monitored effectively.
How to Secure Machine Identities: A Lifecycle Approach
To mitigate risks, organizations must adopt automated, policy driven governance for non-human identities. Here’s how:
1. Discovery & Inventory
Scan systems, code, and cloud environments to detect unmanaged credentials.
2. Classification & Ownership
Tag identities by criticality and assign ownership to ensure accountability.
3. Least Privilege Access
Enforce role based policies grant only necessary permissions.
4. Automated Secret Management
Encrypt & rotate credentials eliminate hardcoded secrets.
5. Continuous Monitoring
Log machine activity and detect anomalies (e.g., unusual API calls).
6. Timely Decommissioning
Remove orphaned identities when systems retire.
The Future: Trust in Automation
As AI, RPA, and autonomous systems grow, so will the complexity of machine identities. Organizations must ensure:
Why Partner with Bridgesoft?
Our identity centric security solutions are designed for modern enterprises, providing:
Machine identities are the backbone of automation secure them with Bridgesoft.
In recent years, the strategic role of Identity and Access Management (IAM) has undergone a dramatic transformation. Once viewed primarily as a back-office function confined to IT departments, identity is now central to the success of digital business initiatives, cybersecurity strategies, and regulatory compliance efforts.
This evolution has been driven by a convergence of forces: the shift to cloud-based infrastructure, the rise of hybrid work, the increasing complexity of access environments, and the growing sophistication of cyber threats. As organizations expand their digital footprint, the challenge of managing who has access to what and ensuring that access is appropriate, secure, and accountable has never been more urgent.
Identity has become the control plane for modern enterprises. It is the common thread connecting employees, contractors, third-party partners, and machine identities to the systems and data they need. And because every interaction starts with identity, it is now a primary target for adversaries. Compromised credentials are consistently cited as a leading cause of breaches across industries.
Organizations are no longer operating within traditional network perimeters. The rapid adoption of SaaS applications, remote work environments, and third-party integrations has pushed access outside the enterprise boundary. As a result, identity is now the last line of defence. Effective identity governance enables real-time visibility and control over access, mitigating the risk of lateral movement in the event of a breach and limiting exposure to sensitive data.
Modern identity programs go far beyond provisioning accounts and managing passwords. When aligned with broader business objectives, IAM can accelerate user onboarding, streamline compliance reporting, reduce operational overhead, and improve the user experience.
For example, by integrating identity systems with HR platforms, access can be automatically assigned and revoked as users join, move, or leave the organization. This reduces manual effort and human error, while ensuring users have the right access at the right time. Additionally, advanced capabilities like identity analytics and AI-powered anomaly detection enable security teams to proactively respond to access-related risks helping to shift identity from a reactive function to a strategic advantage.
A successful identity program requires coordination across multiple stakeholders security teams, IT operations, HR, compliance, and business unit leaders. Yet in many organizations, these functions operate in silos. IAM implementations often stall due to unclear ownership, conflicting priorities, or poor communication between departments.
Establishing a cross-functional identity governance model can help bridge these gaps. This means bringing stakeholders together to define common objectives, clarify roles and responsibilities, and establish metrics that align with broader business goals. With the right collaboration, IAM can become a unifying force rather than a point of friction enabling secure
As digital ecosystems grow more complex and interconnected, identity will continue to play a defining role in shaping enterprise risk and opportunity. Organizations that recognize IAM as a strategic asset and invest in building mature, outcome-driven identity programs will be better positioned to thrive in a fast-changing landscape.
Ignoring identity’s expanding role comes at a cost. Whether it’s through compliance gaps, delayed onboarding, or increased exposure to threats, treating IAM as a low-priority technical project is a missed opportunity. The organizations that succeed will be those that elevate identity to the level of strategic infrastructure on par with cloud, data, and cybersecurity.
Partner with Bridgesoft to Transform Identity into Opportunity
At Bridgesoft, we understand that identity is more than just a technical control, it's the foundation of trust, security, and agility in today’s digital enterprise. With deep expertise in IAM strategy, deployment, and governance across industries, we help organizations turn identity challenges into business enablers. Whether you’re modernizing your access architecture, achieving compliance, or preparing for the next phase of digital growth, Bridgesoft delivers customized, scalable solutions to meet your unique needs.