Author: Bridgesoft
-
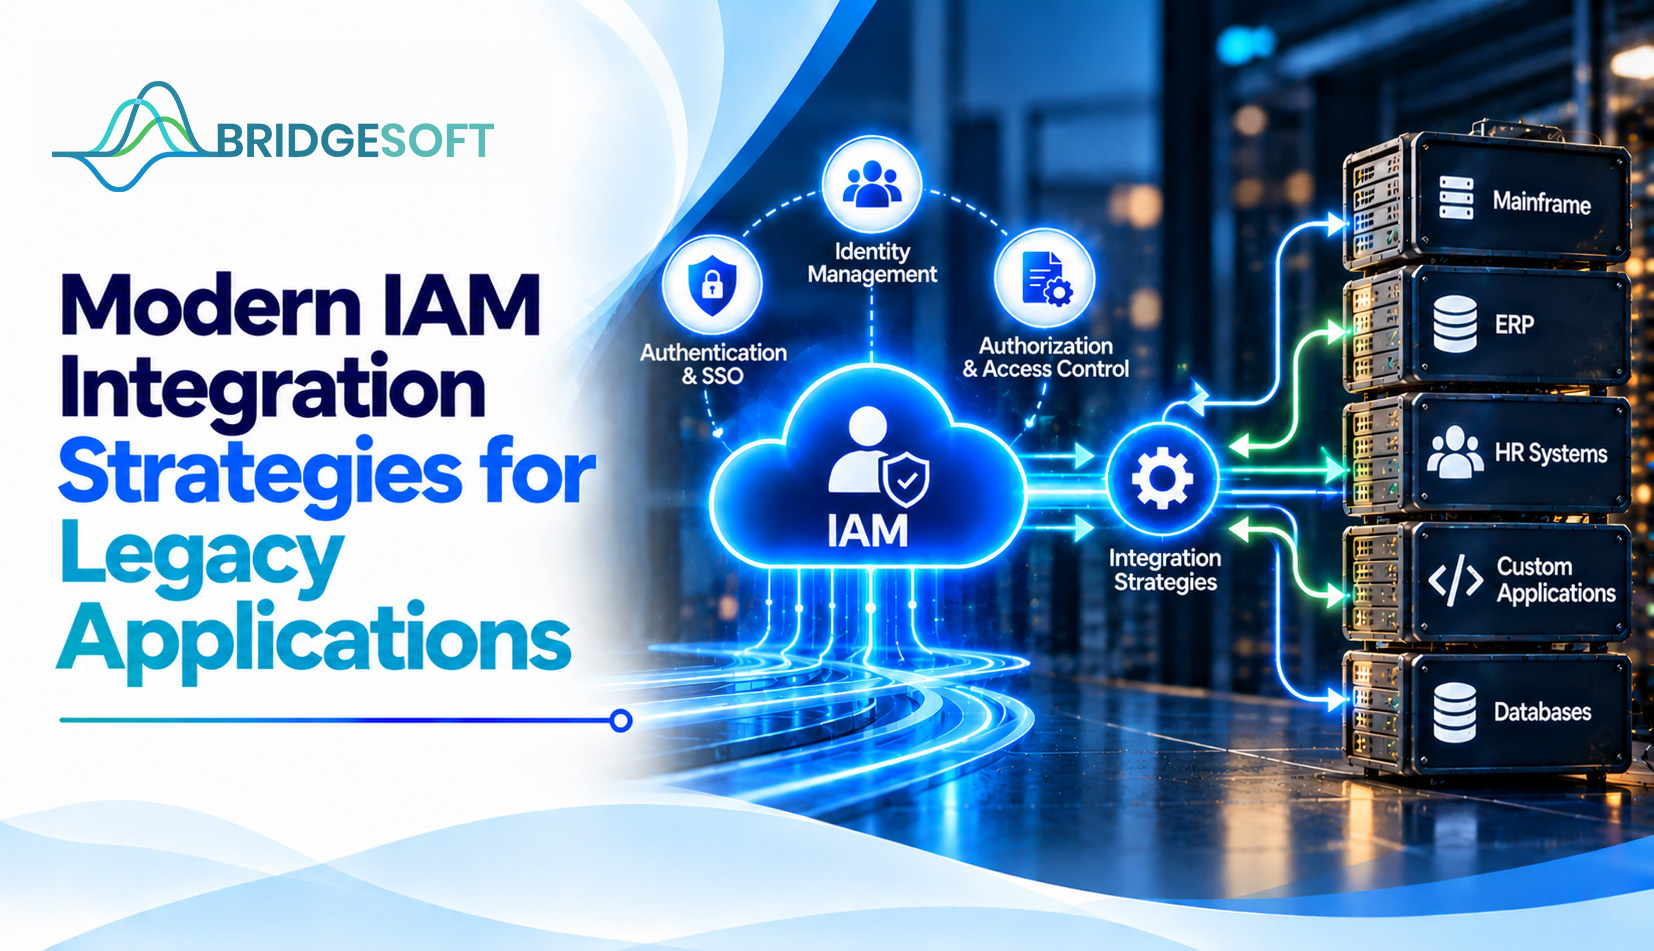
Modern IAM Integration Strategies for Legacy Applications
Legacy applications rarely sit neatly within a modern identity architecture. A finance platform may expose a database, but no API; a manufacturing system may use local accounts; and a business-critical web application may not support current federation standards. The challenge is not simply connecting each system. It is choosing an integration pattern that is secure,…
-
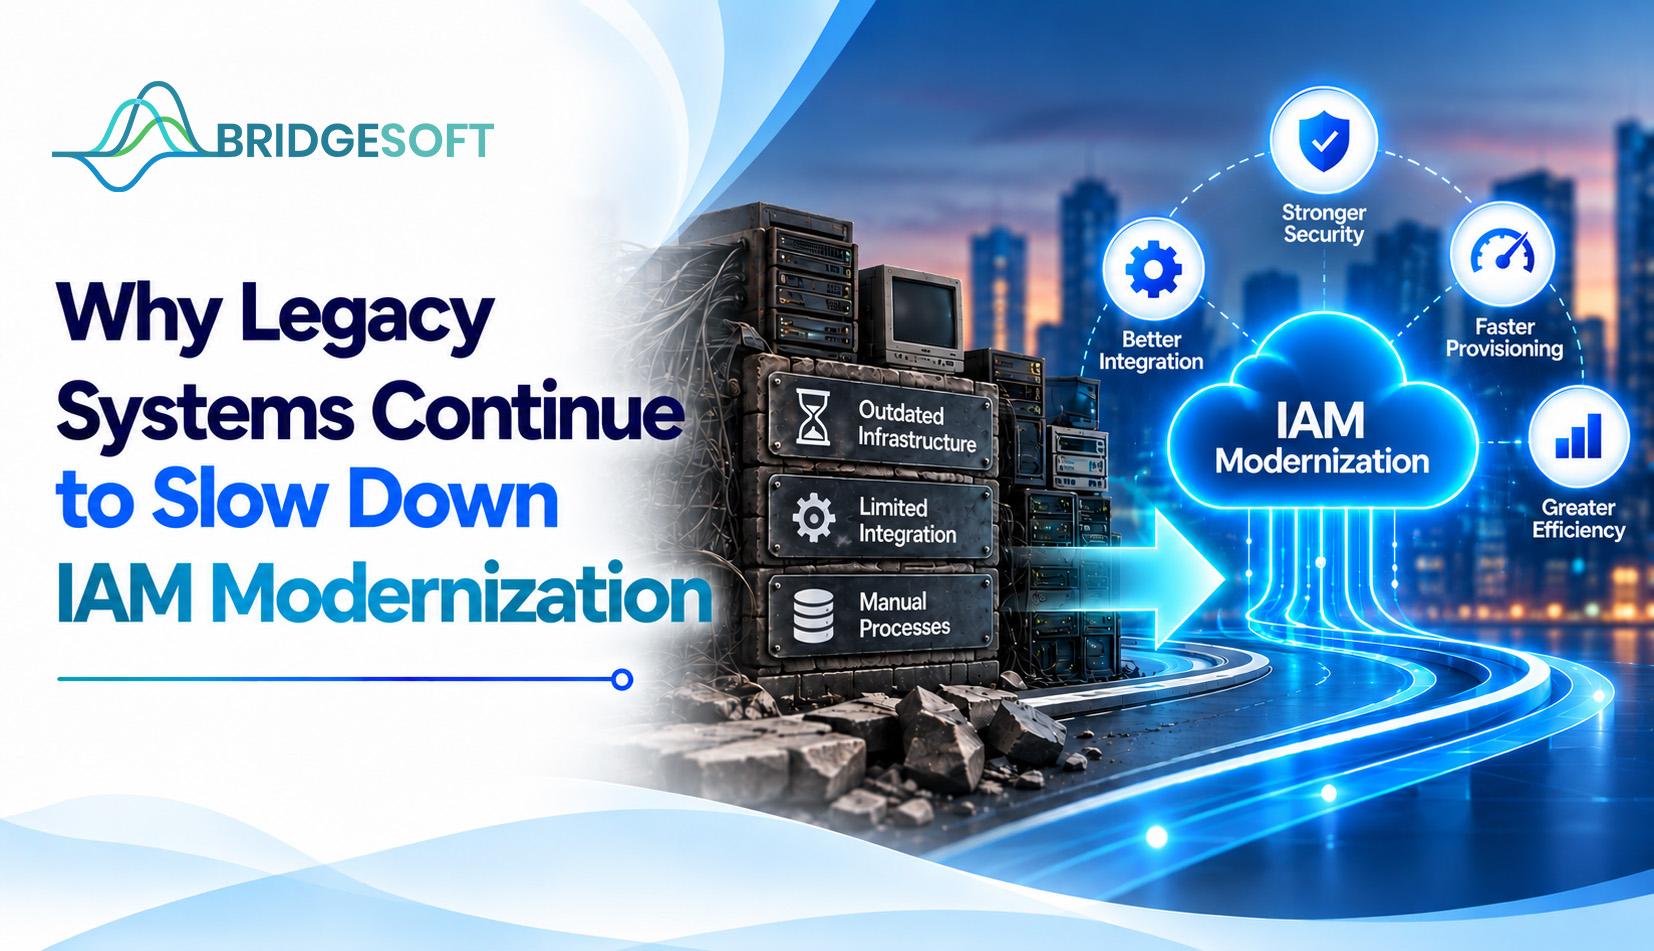
Why Legacy Systems Continue to Slow Down IAM Modernization
Before an audit, a CISO asks a simple question: who still has access to the old finance application? Because the system maintains its own user list, no one owns it anymore, and the individual who created its roles departed years ago. This is the everyday reality of IAM modernization in most large organizations, and it…
-
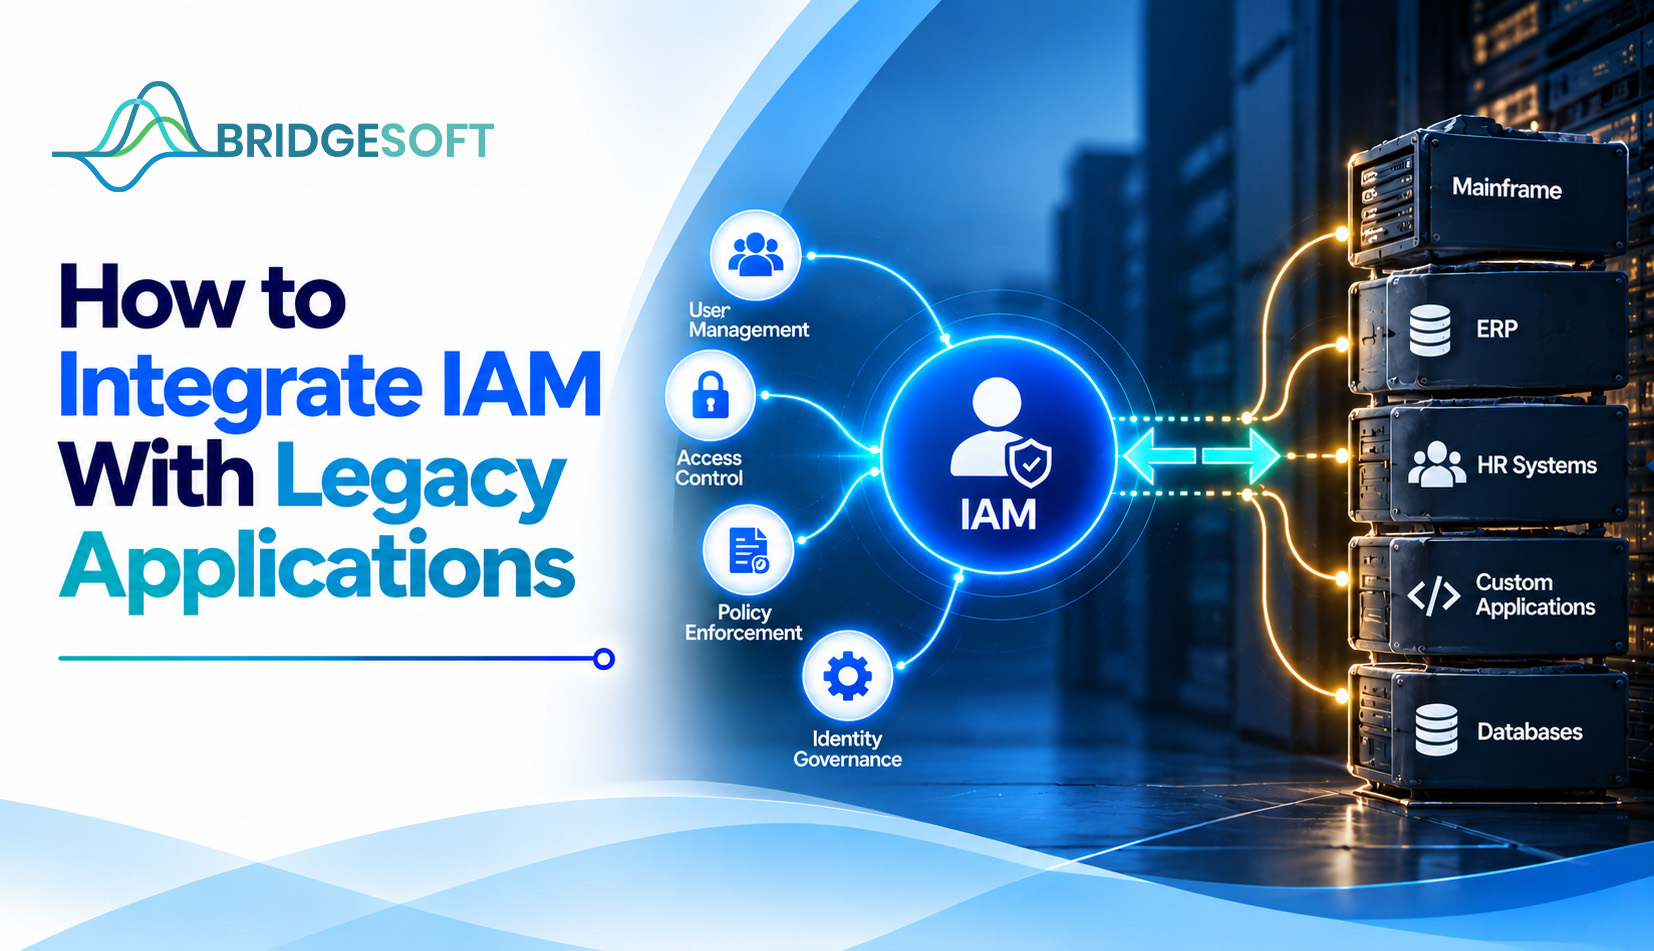
How to Integrate IAM With Legacy Applications
Somewhere in your environment, a 15-year-old application still handles something important, such as payroll, claims, or plant scheduling. It has its own user database and its own passwords. Nobody wants to touch it because nobody is sure what will break if they do. Application auditors usually ask about it first. Integrating identity and access management…
-
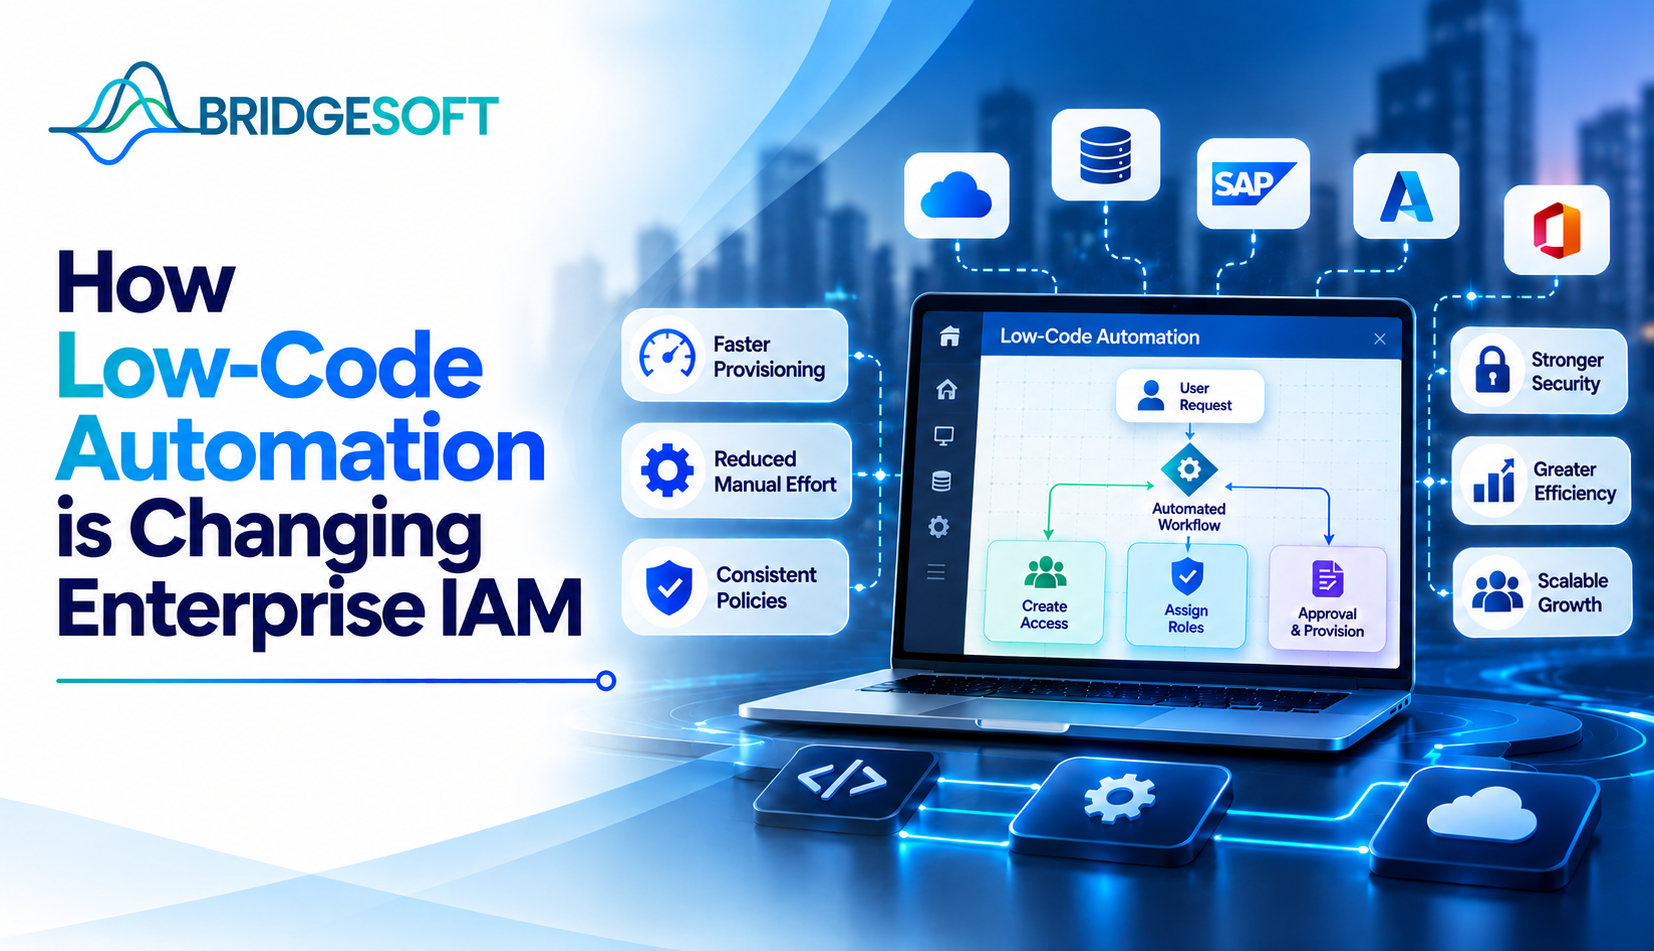
How Low-Code Automation Is Changing Enterprise IAM
A new hire starts on Monday. By Wednesday, she still can’t open the finance system. The IT staff uses a spreadsheet to determine who approves what, and her manager has resubmitted the access request twice. Multiply that by every hire, transfer, and contractor in a 10,000-person company, and you have the quiet cost of manual…
-
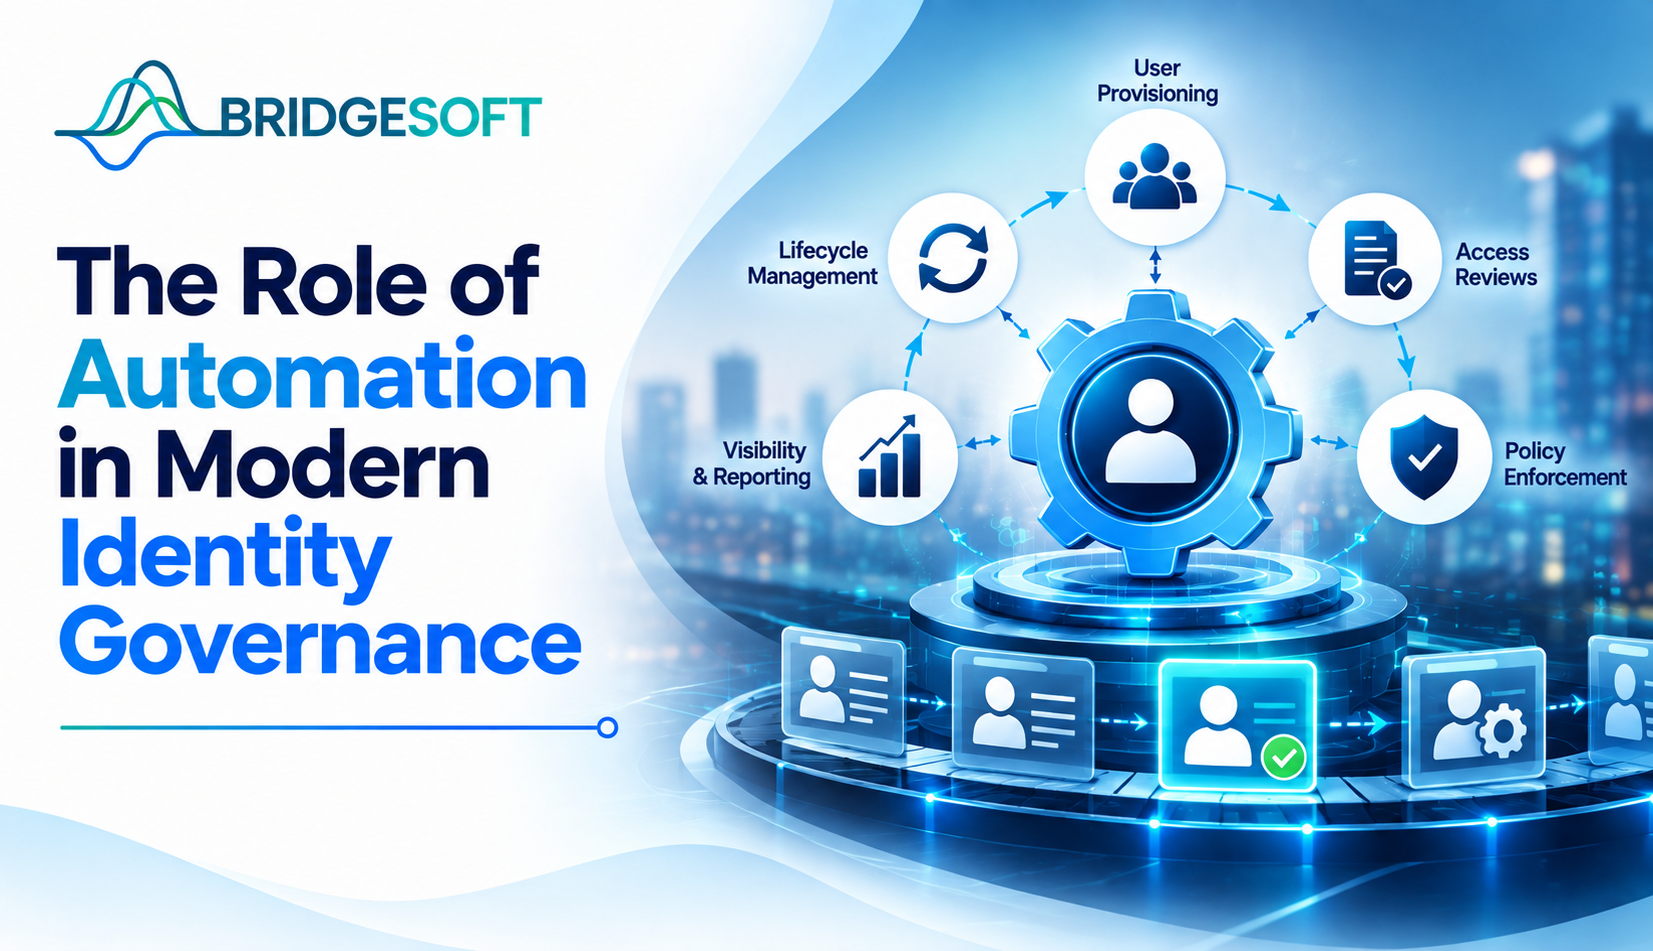
The Role of Automation in Modern Identity Governance
An auditor asks for evidence that every terminated employee lost access within a defined window. The answer lives in a spreadsheet, three ticketing queues, and the memory of one overworked IT administrator. If that sounds familiar, the problem isn’t your team. Manual processes can’t keep pace with the number of identities, applications, and cloud services…
-
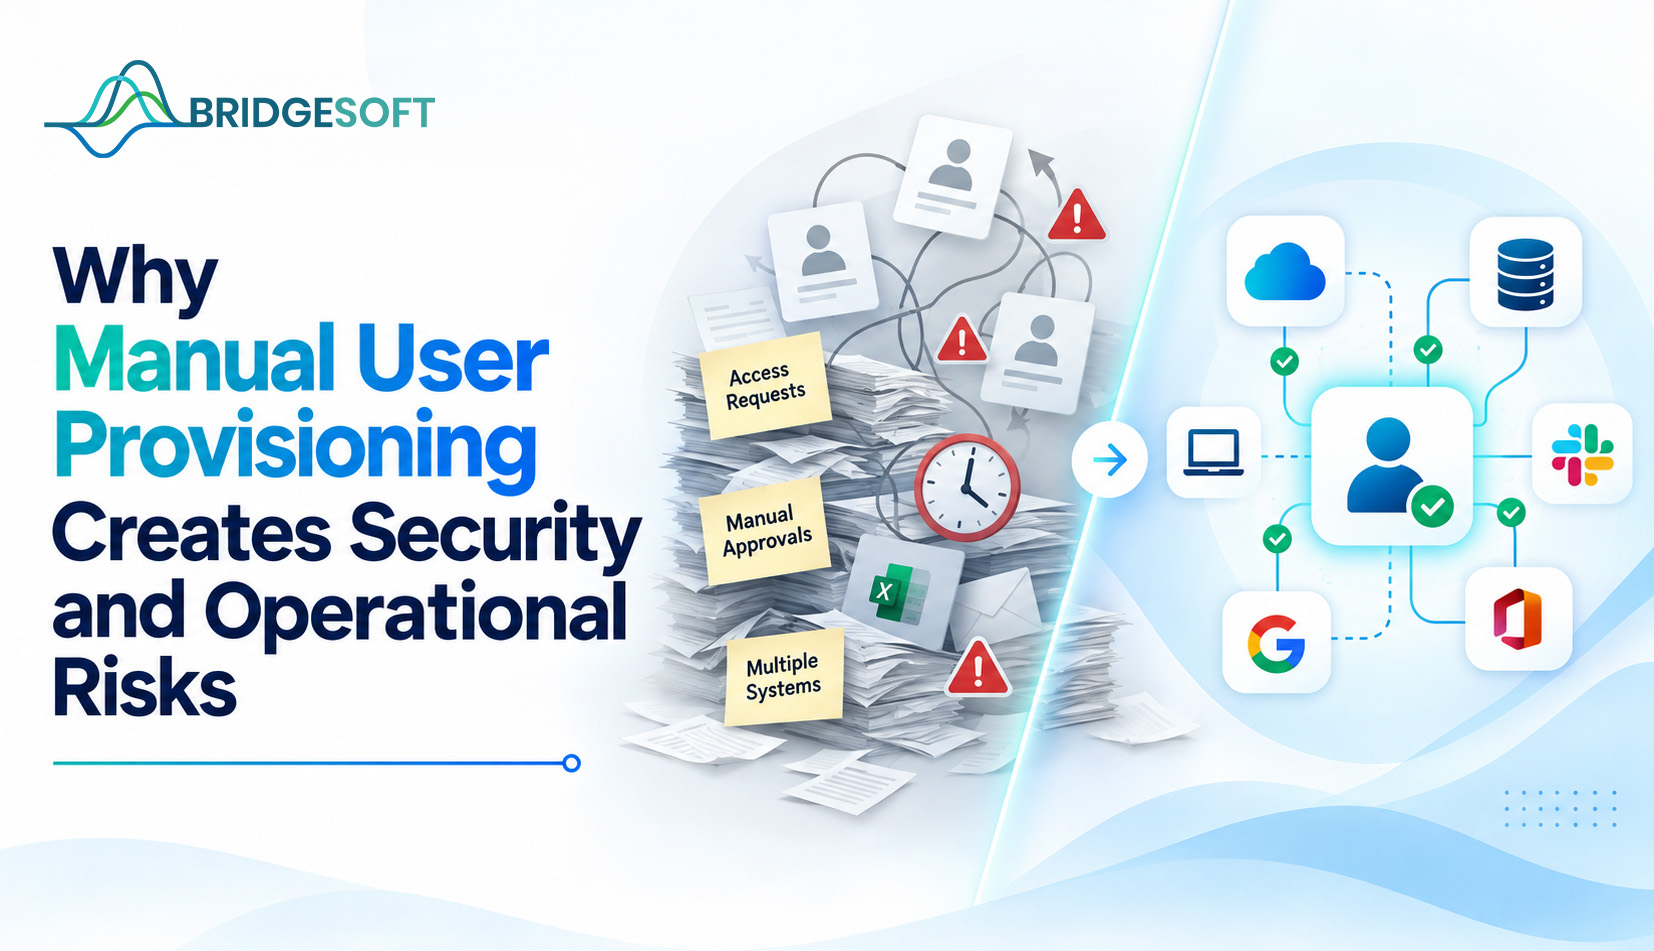
Why Manual User Provisioning Creates Security and Operational Risks
A new hire starts on Monday. By Wednesday, they still can’t access the CRM because their access request is sitting in someone’s inbox behind forty other tickets. Meanwhile, an employee who left the company three months ago still has an active VPN account nobody remembered to disable. Both problems trace back to the same root…
-
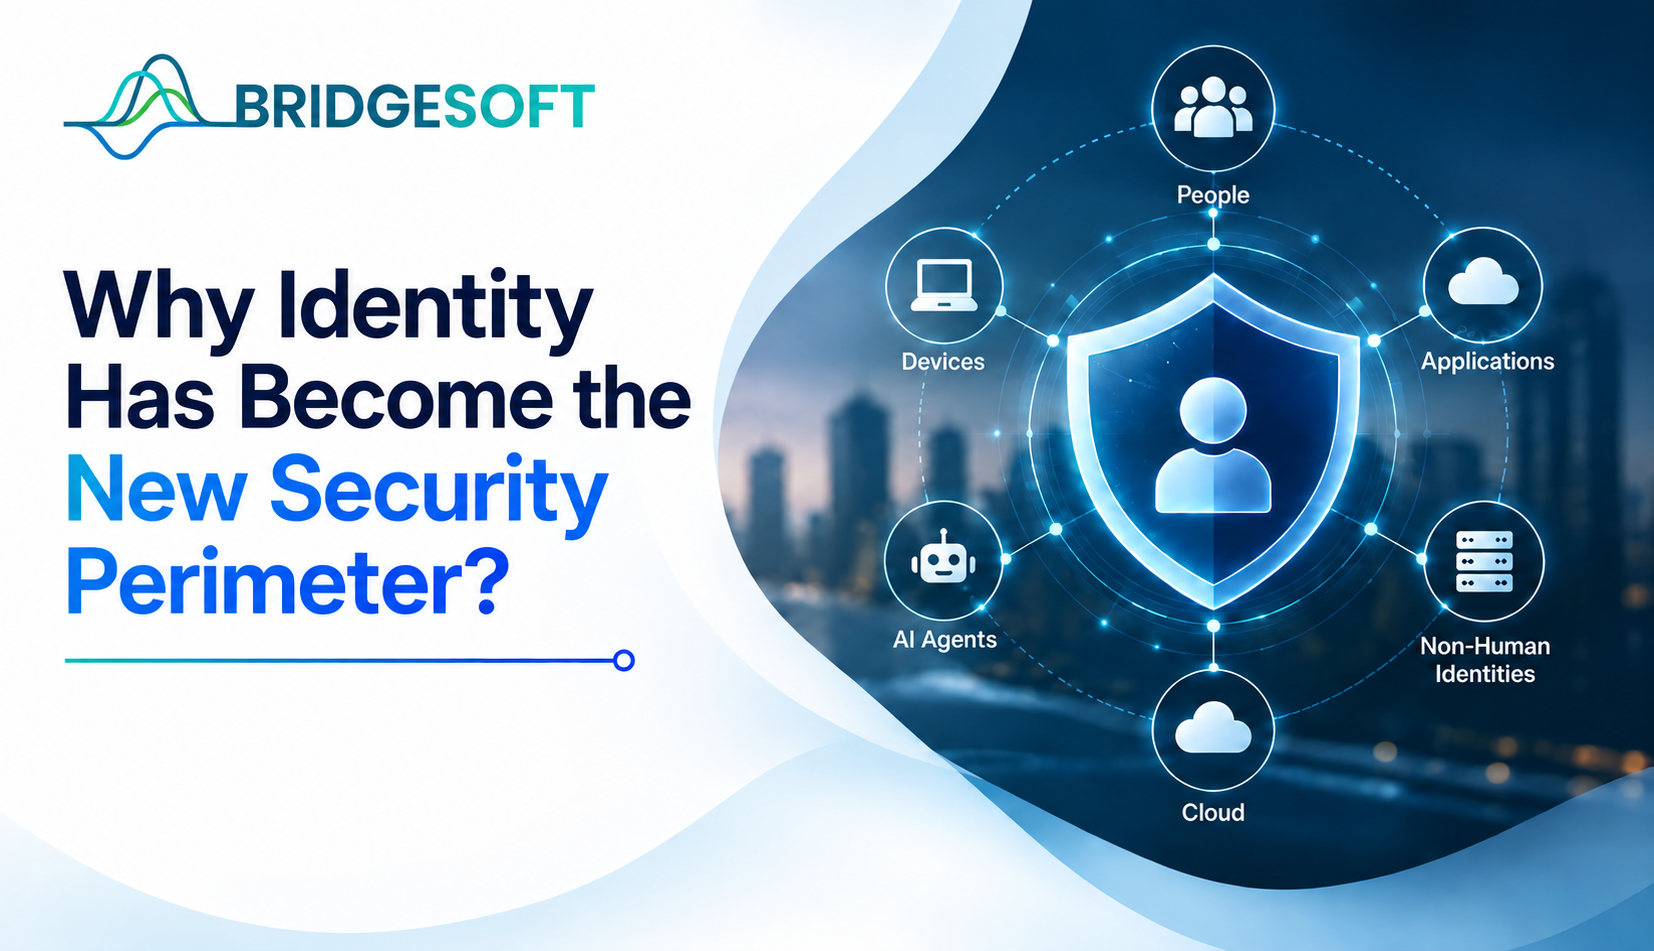
Why Has Identity Become the New Security Perimeter?
A firewall can protect a network boundary. But what happens when employees work from home, applications run across multiple clouds, contractors need temporary access, and software and AI agents automatically interact with business systems? The traditional network perimeter becomes much harder to define. That is why identity has become a central security control point. Modern…
-
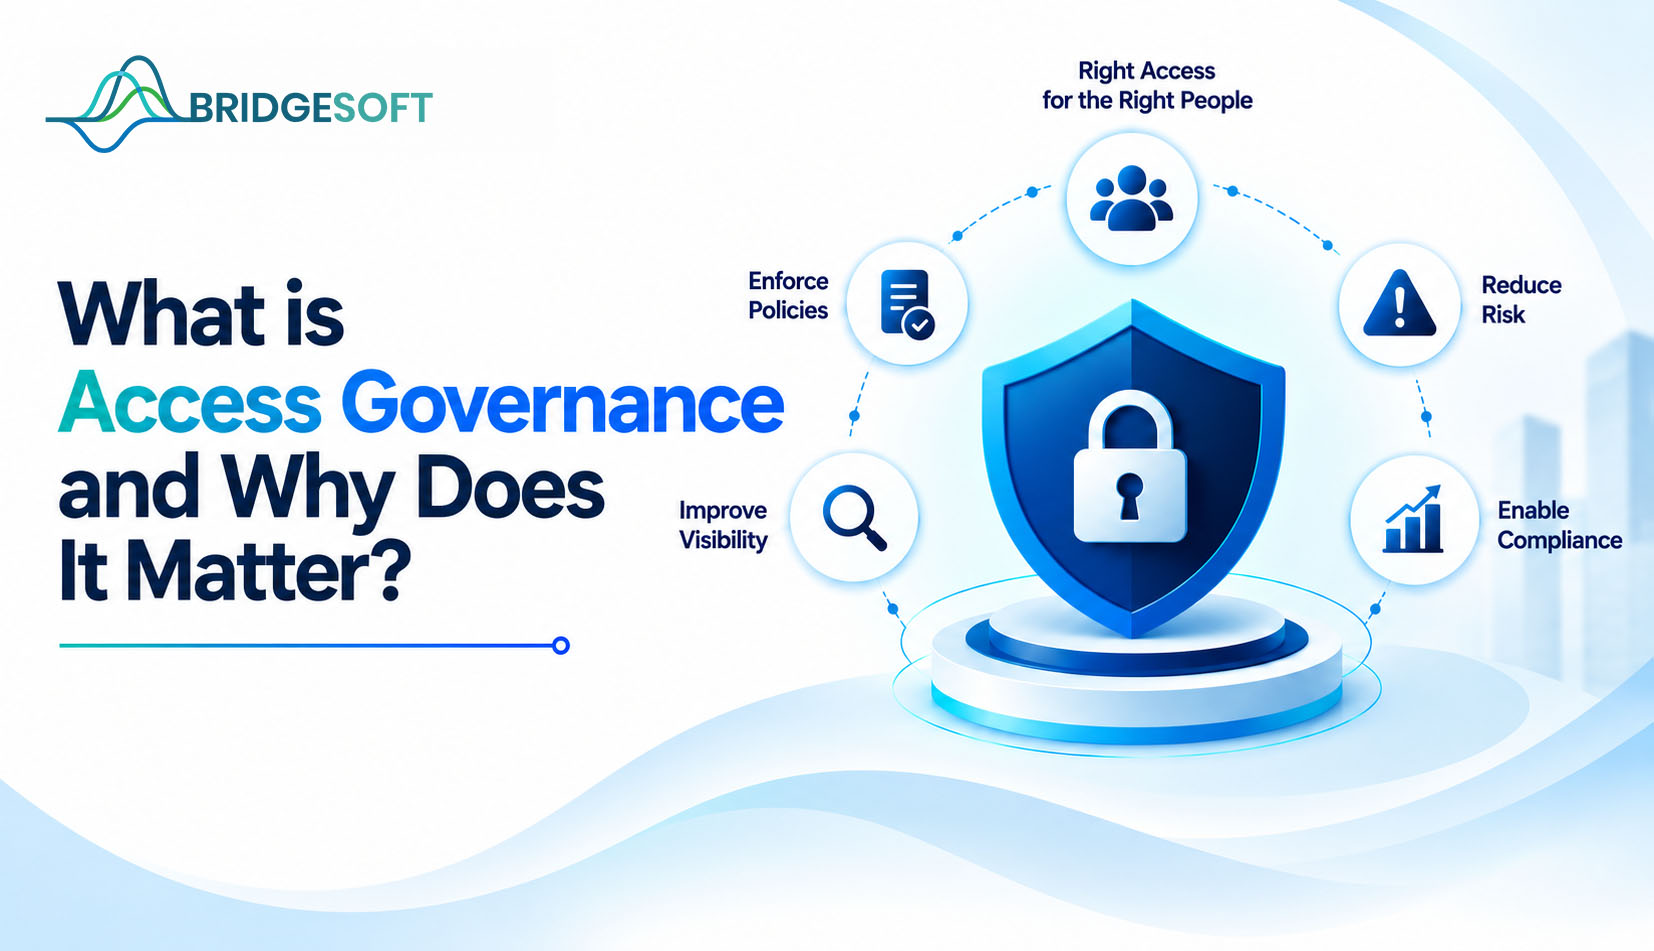
What is Access Governance and Why Does It Matter?
An employee moves from marketing to finance. Nobody removes his/her marketing system access because nobody owns that step. Eighteen months later, he/she has standing access to customer campaign data, the finance reporting system, and, because a contractor project briefly needed his/her help, a vendor portal he/she hasn’t logged into in a year. None of this…
-
Why Most IAM Implementations Run Over Timeline and How to Avoid It
A CISO signs off on a 9-month Identity and Access Management rollout. Six months later, the project team is still reconciling duplicate identities in HR data, legal is asking why contractors weren’t scoped into the original access model, and the “go-live” date has quietly moved twice. None of this makes headlines. It just makes budgets…
-
Why Identity Security Must Evolve for the AI Era
Artificial intelligence is moving into the core of how businesses operate. What started as pilots and proofs of concept is quickly becoming part of everyday work. AI assistants, autonomous agents, intelligent applications, and automation platforms now access systems, retrieve information, interact with APIs, trigger workflows, and carry out tasks that once required direct human involvement.…